ApeX C2 The only agentic and OPSEC focused command and control framework for red teams.
Native AI operator via MCP. On-agent Lua VM for post-exploitation that runs in a single task. Compile-time OPSEC with clean, image-backed call stacks by architecture, not gadgetry. Deploy air-gapped, at the edge, or in the cloud.
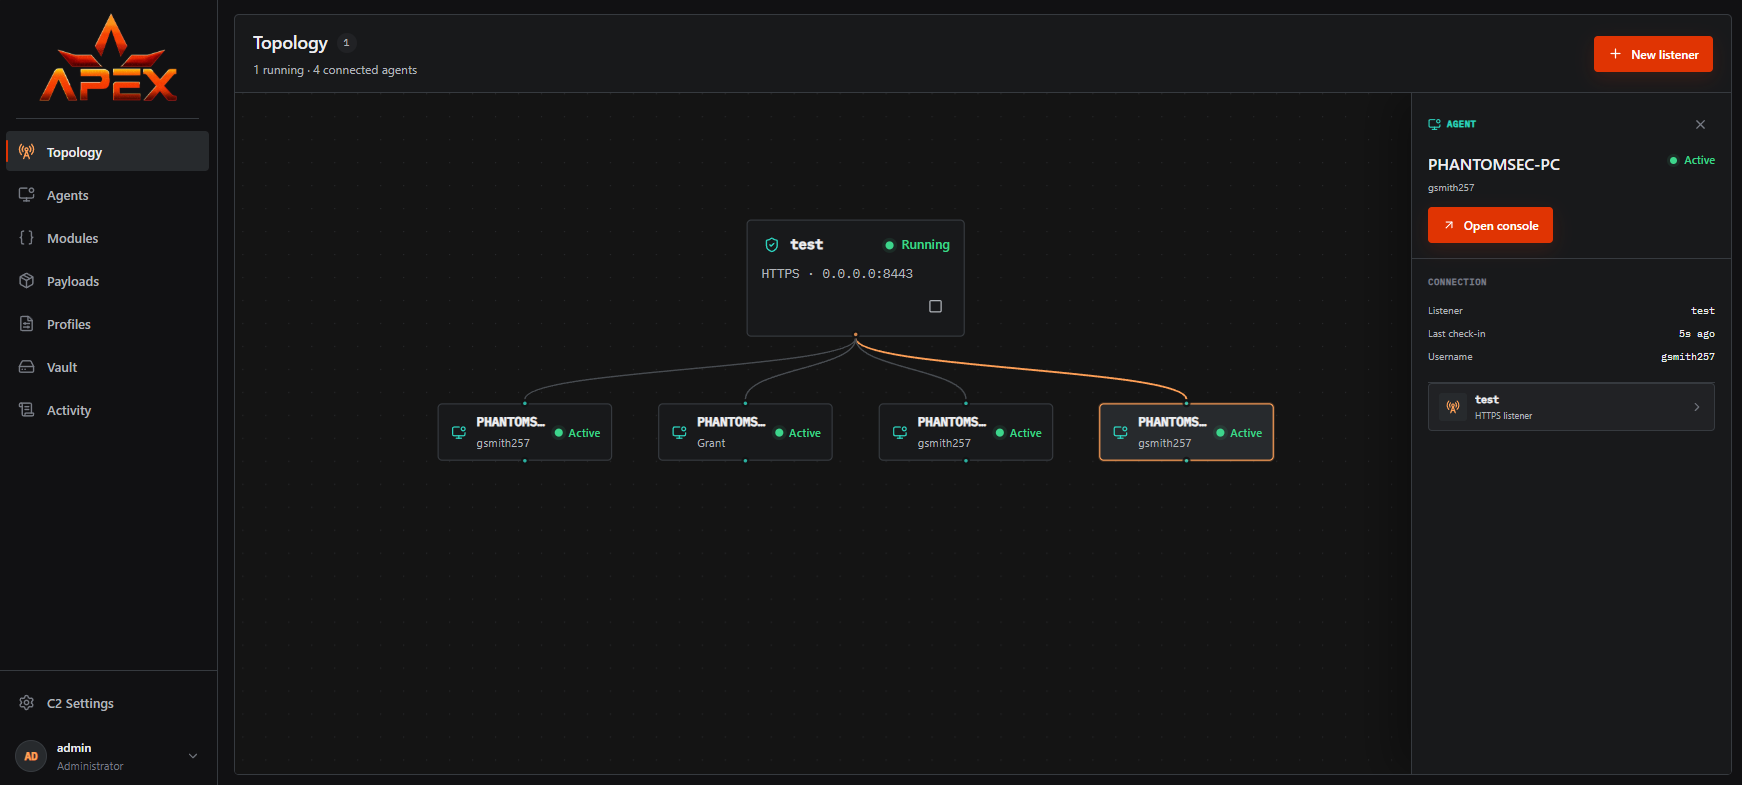
ApeX C2 is a post-exploitation command and control framework built for red team operations. A Zig-compiled agent paired with a modern web operator interface, supporting Windows, Linux, and macOS targets. The entire stack deploys as a Docker Compose bundle, including fully air-gapped and edge deployment modes. No internet connectivity required on the operations host.
What makes ApeX different
AI operator via MCP
Connect any MCP-compatible LLM (Claude Code, Cursor, Codex) to the teamserver. Scoped tokens let an AI reason through enumeration, write and run modules, and adapt based on results. Every action is logged. Reasoning-driven autonomy, not scripted playbooks.
On-agent Lua VM
A sandboxed LuaJIT VM runs directly on the agent with a full post-exploitation API: filesystem, processes, tokens, registry, services, crypto, network, named pipes. LuaJIT FFI gives direct Win32 access. Complex recon in a single task, not a dozen heartbeats.
OPSEC by architecture
Compile-time string encryption, API hashing, indirect syscalls, mixed boolean arithmetic obfuscation, RWX-less code paths, sleep encryption of both code and heap, spoofed sleep stacks. Per-build polymorphism seed ensures no two builds share byte-level patterns.
BOF and BOF-PE execution
Full Cobalt Strike BOF compatibility, COFF and BOF-PE formats auto-detected at runtime. Sensitive Win32 APIs from BOFs are intercepted and routed through the agent OPSEC infrastructure, producing clean, image-backed call stacks.
Deploy anywhere
Local .NET Aspire development. Docker Compose production. Offline bundles for air-gapped sites with automated smoke tests. Distributed edge listeners with per-edge mTLS bootstrap. No internet required on the ops host.
An agent, acting on one instruction
operator> on WIN-7XQ2, find a path to SYSTEM without
          touching disk and without mimikatz-style apis

agent>    reading Lua api references
          done.

agent>    drafting module priv_check_v1.lua
          scope: scan token privileges, enumerate
          SYSTEM services, probe named-pipe
          impersonation candidates
          mode: non-destructive, no process spawn

agent>    upload_lua_module(WIN-7XQ2, priv_check_v1)
          ok, module id f3a7...2c81

agent>    execute_lua_module(WIN-7XQ2, priv_check_v1)
          SeImpersonatePrivilege: enabled
          named-pipe surfaces visible to agent:
            \pipe\spoolss   spoolsv.exe   SYSTEM
          path identified: named-pipe impersonation
          via spoolsv
          dwelling for review in agent console.
Red team leads
- Reduce C2 chatter: on-agent Lua does in one task what other C2s do in ten round-trips.
- Clean, image-backed stacks by architecture. CET compatible without gadget chaining.
- Full Cobalt Strike BOF compatibility. Your existing library ports day one.
- Modern web UI with real-time push, WebAuthn and passkeys. No legacy Java client.
- 25+ MCP tools let an AI run recon or stage tools under your supervision.
Engineering leaders
- The only C2 with a native agentic AI operator interface. Scoped tokens, immutable audit, instant revocation.
- Per-build polymorphism from a single seed. No shared signatures across customers.
- Air-gapped and edge deployment with automated build and test pipelines. Deploy where your clients require.
- CI/CD-grade quality bar: AgentSim deterministic simulator, 20 Playwright E2E specs, Docker integration tests.
- WebAuthn and passkey auth. Two roles. Session-level revocation. No shared passwords.
Access and availability
United States, United Kingdom, EU, Australia, Canada, Iceland, Japan, New Zealand, Norway, Switzerland (including Liechtenstein).
Enquiries outside the immediately-available regions are subject to extended vetting.
Belarus, Russia, Ukraine, Central African Republic, China, North Korea, Iran, Iraq, Lebanon, Republic of the Congo, Libya.
Explore further
AI operator via MCP
25+ MCP tools across 15 scopes. See how Claude Code, Cursor, or Codex drive engagements autonomously, with full audit.
OPSEC in depth
Indirect syscalls, MBA obfuscation, sleep encryption, CET-compatible stacks, BOF API proxying. The full evasion suite with build-time knobs.
How ApeX compares
Feature-by-feature matrix against Cobalt Strike 4.13, Brute Ratel C4 2.3, and Nighthawk 1.0.
Request ApeX access
ApeX is sold through a vetted-access process. Tell us about your team and we will personally review your request.
Questions before you request access?
Book time on our calendar, or email us at info@phantomsec.tools.